Find what they're building
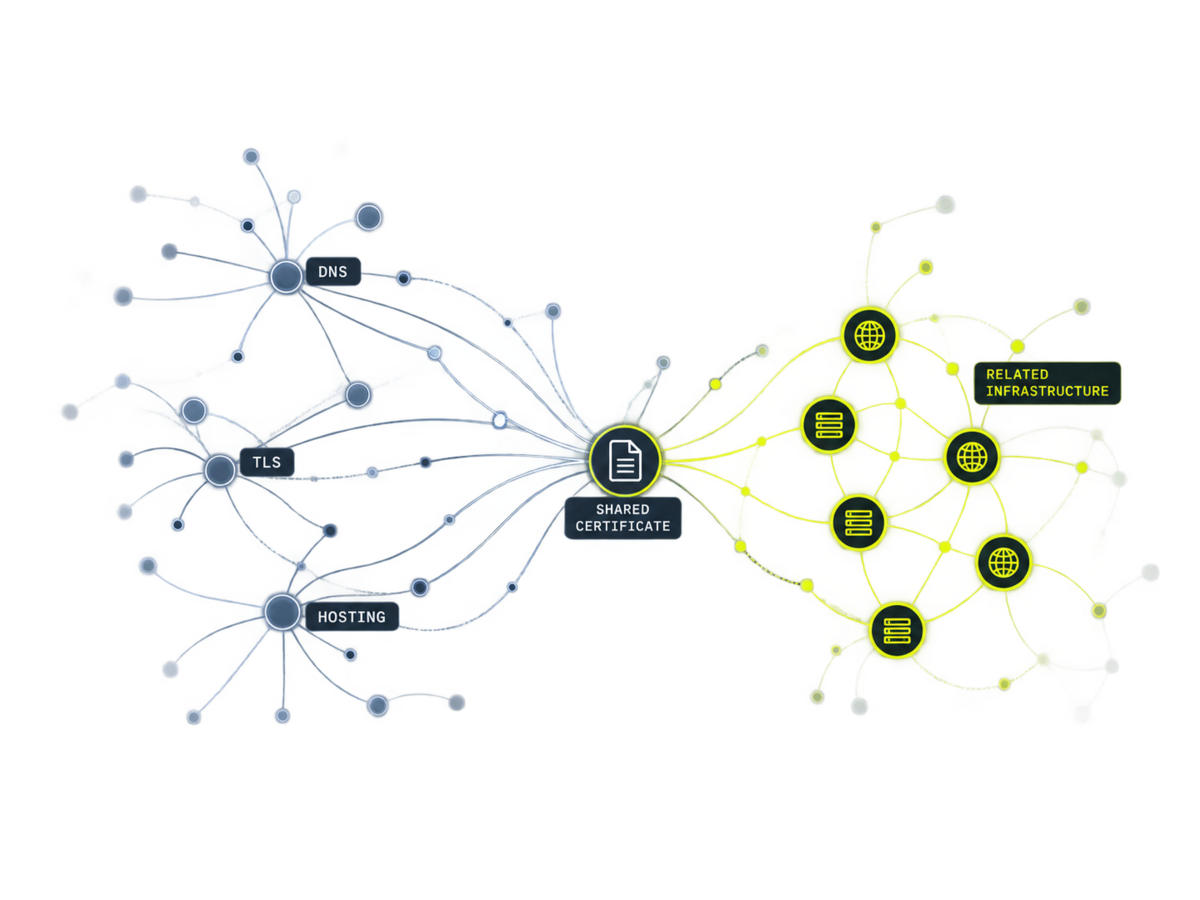
We actively investigate attacker-operated domains, hosting, DNS, certificates and infrastructure relationships beyond a customer's own telemetry.
Adversary hunting ↗
We built Lab539 to challenge that imbalance: hunting for adversary infrastructure before it's put to use, and helping defenders act on what we find.
Detection and response remain essential. But adversaries don't wait until execution to start work, and neither should defenders. Their preparation creates opportunities to recognise—and sometimes prevent—an attack before it reaches its target.
We actively investigate attacker-operated domains, hosting, DNS, certificates and infrastructure relationships beyond a customer's own telemetry.
Adversary hunting ↗
We investigate the relationships, roles and evidence behind what we find, so customers can distinguish indicators worth monitoring from those suitable for preventative action.
Intelligence feeds ↗
Put the intelligence to work through the controls you already own. AiTM Feed supports preventative identity controls today, while Disrupt is available in early access for organisations looking to bring our intelligence and supported integrations together.
Meet Disrupt ↗Detect an attack early, and you can respond.
Find its infrastructure first and you can stop the attack before it starts.
Our first-hand research informs the intelligence we deliver and the defences we help organisations put in place. Whether you need a standalone feed, a dedicated adversary hunt, an established AiTM prevention service or early access to Disrupt, there are different ways to work with Lab539.
Hunt and track AiTM infrastructure, with preventative integrations already available to customers.
Explore AiTM Feed ↗INTELLIGENCE / DELIVERY
Context-rich indicators for teams that prefer to ingest and operationalise intelligence in their own platforms.
Explore feeds ↗RESEARCH / BESPOKE
Dedicated investigations of campaigns, operators and infrastructure relevant to your organisation, with ongoing delivery.
Commission a hunt ↗PLATFORM / BY INVITATIONOriginal adversary intelligence and supported defensive integrations, brought together in a platform available by invitation in early access.
Request an invitation ↗Our AiTM Non-Incident Report documents authentication prevented by a customer's Conditional Access policy using Lab539-supplied infrastructure intelligence. That is the difference between reporting a threat and having an existing control act on it.
Original investigations of adversary infrastructure, attack preparation and the practical limits of security controls.
Browse the blog ↗A real attempted AiTM compromise stopped by preventative Conditional Access controls.
Read researchWhy intelligence discovered during adversary preparation deserves to be recognised and acted on.
Read researchAn investigation into bank-themed fraud sites, signed malware, AnyDesk and unattended ScreenConnect access.
Read research